Perform Real-Time Security Monitoring and Detect Suspicious Activities

Business Scenario
Welcome!
You are a SOC Analyst at CyberSecure Solutions. Your organization continuously monitors its systems and network for suspicious activities.
Your task is to monitor security events in real time, identify suspicious behavior, investigate alerts, and determine whether the activity requires a security response.
Pre-Lab Preparation
Topic : SOC Fundamentals
1) Introduction to Security Operations Center (SOC)
2) Roles and responsibilities of a SOC analyst
3) Security monitoring fundamentals
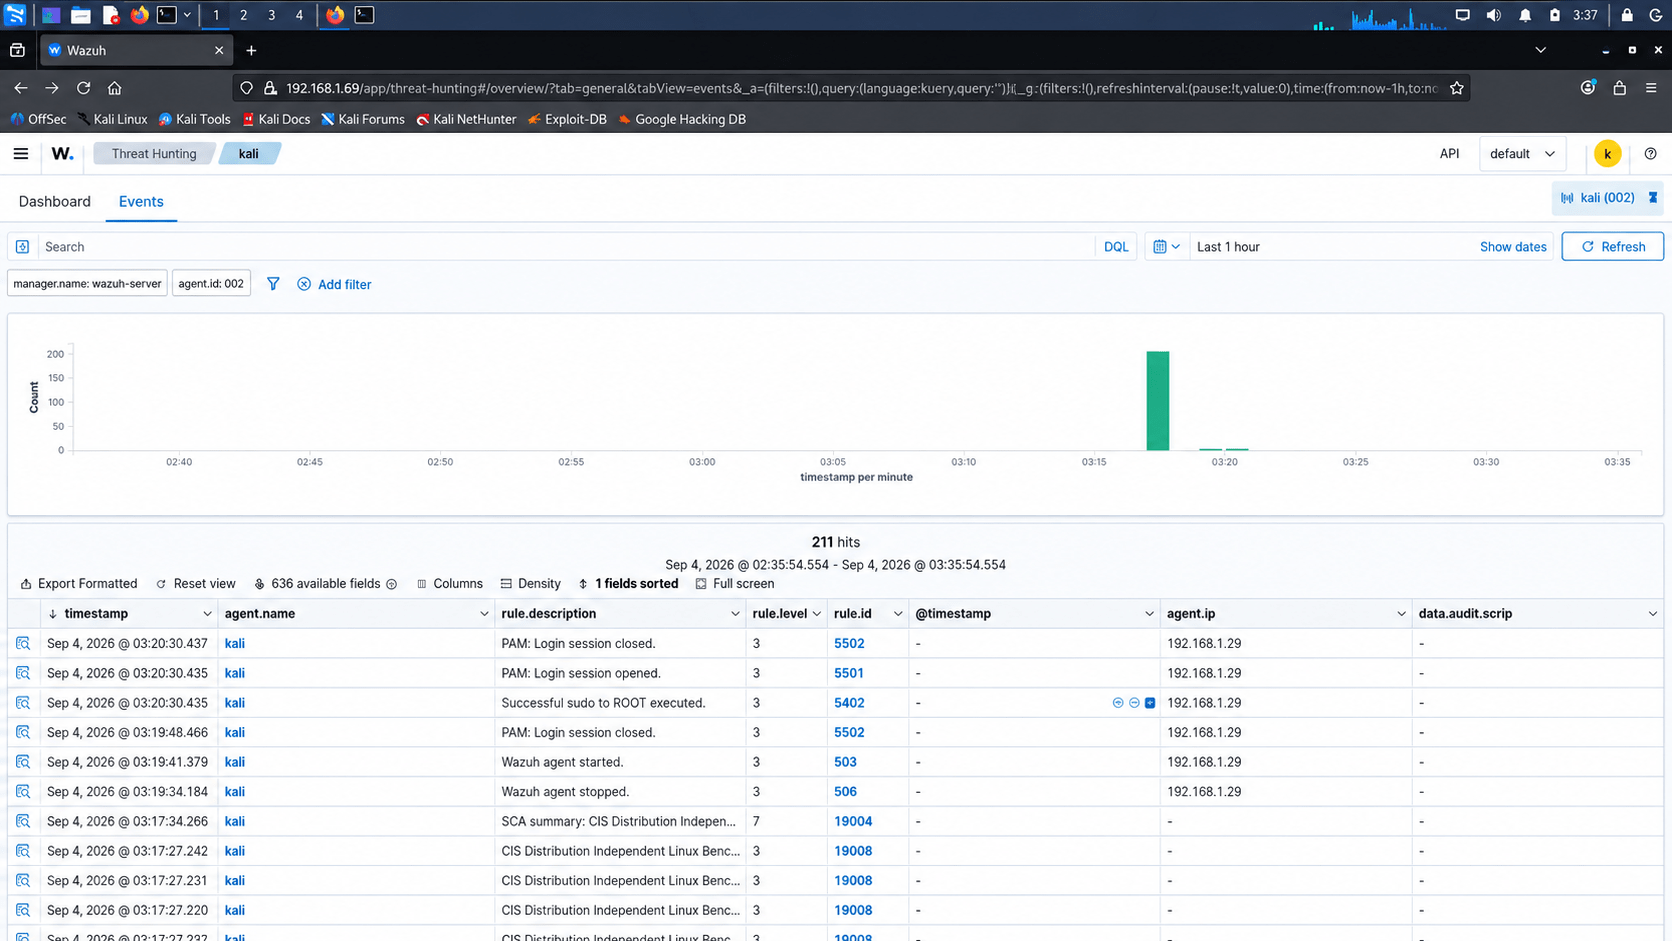
Task 1: Monitor Security Events
Learn how a SOC analyst monitors events in real time.
1
Steps
a
-
Start the test endpoint.
-
Open the SIEM dashboard.
-
Navigate to the Events/Alerts section.
-
Observe incoming security events.
-
Record:
-
Time
-
Source
-
Event type
-
Username
-
Severity
-
Expected Output
b
Task 2: Generate Suspicious Activity
Generate controlled security events in the lab environment.
1
a
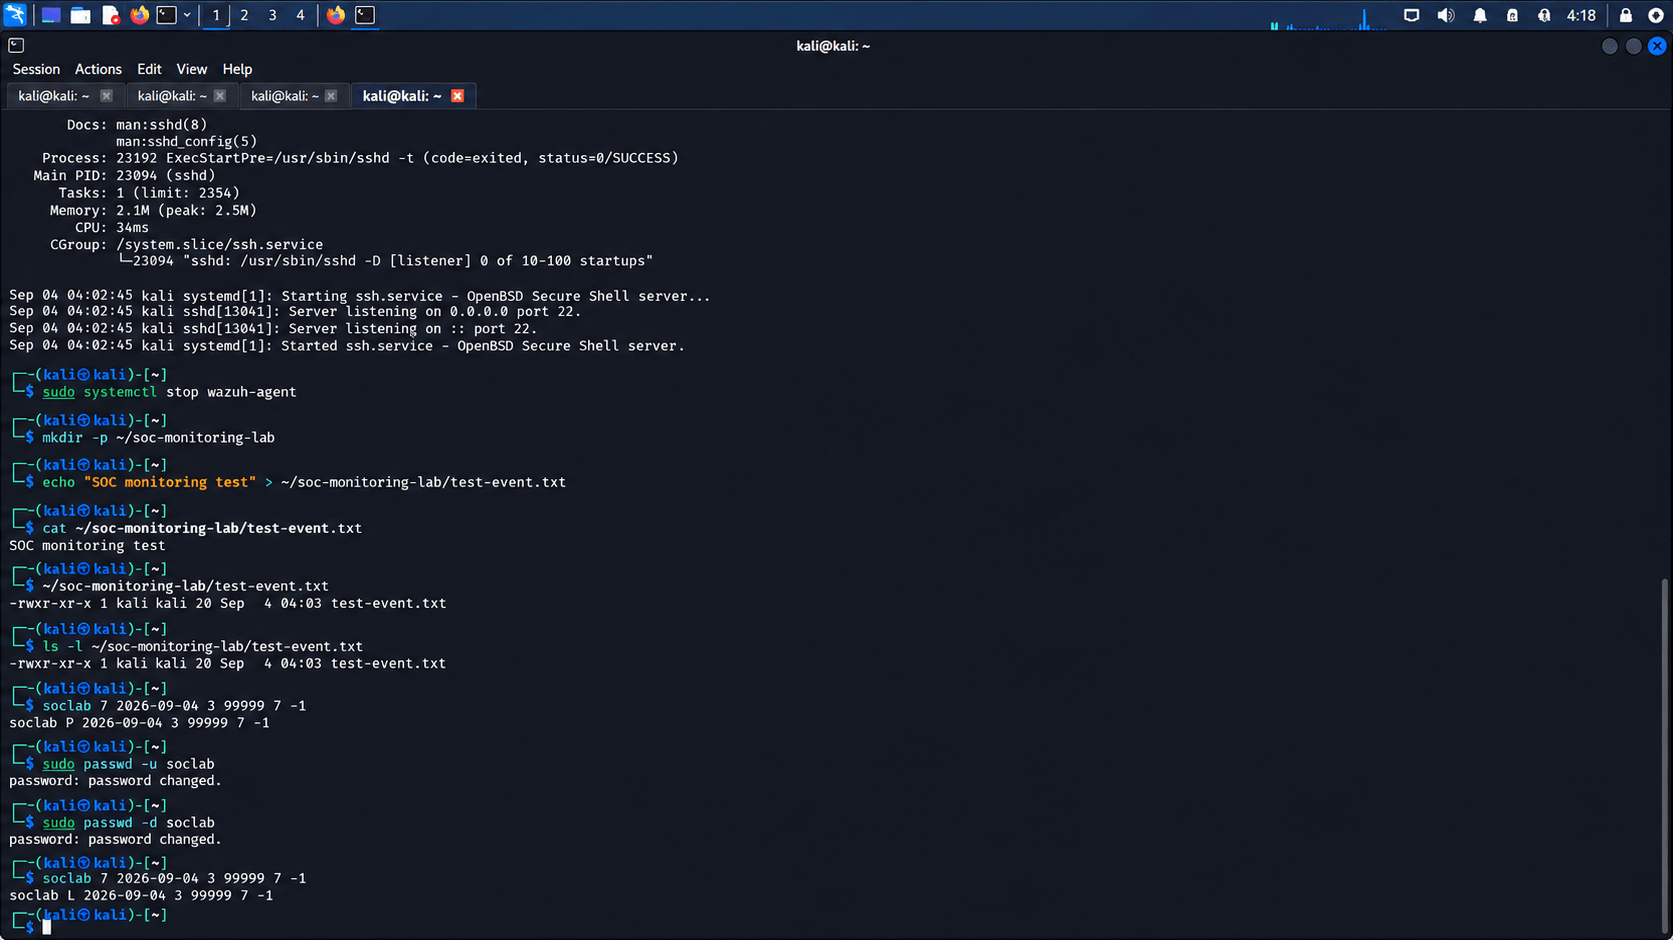
-
Use the authorized test machine.
-
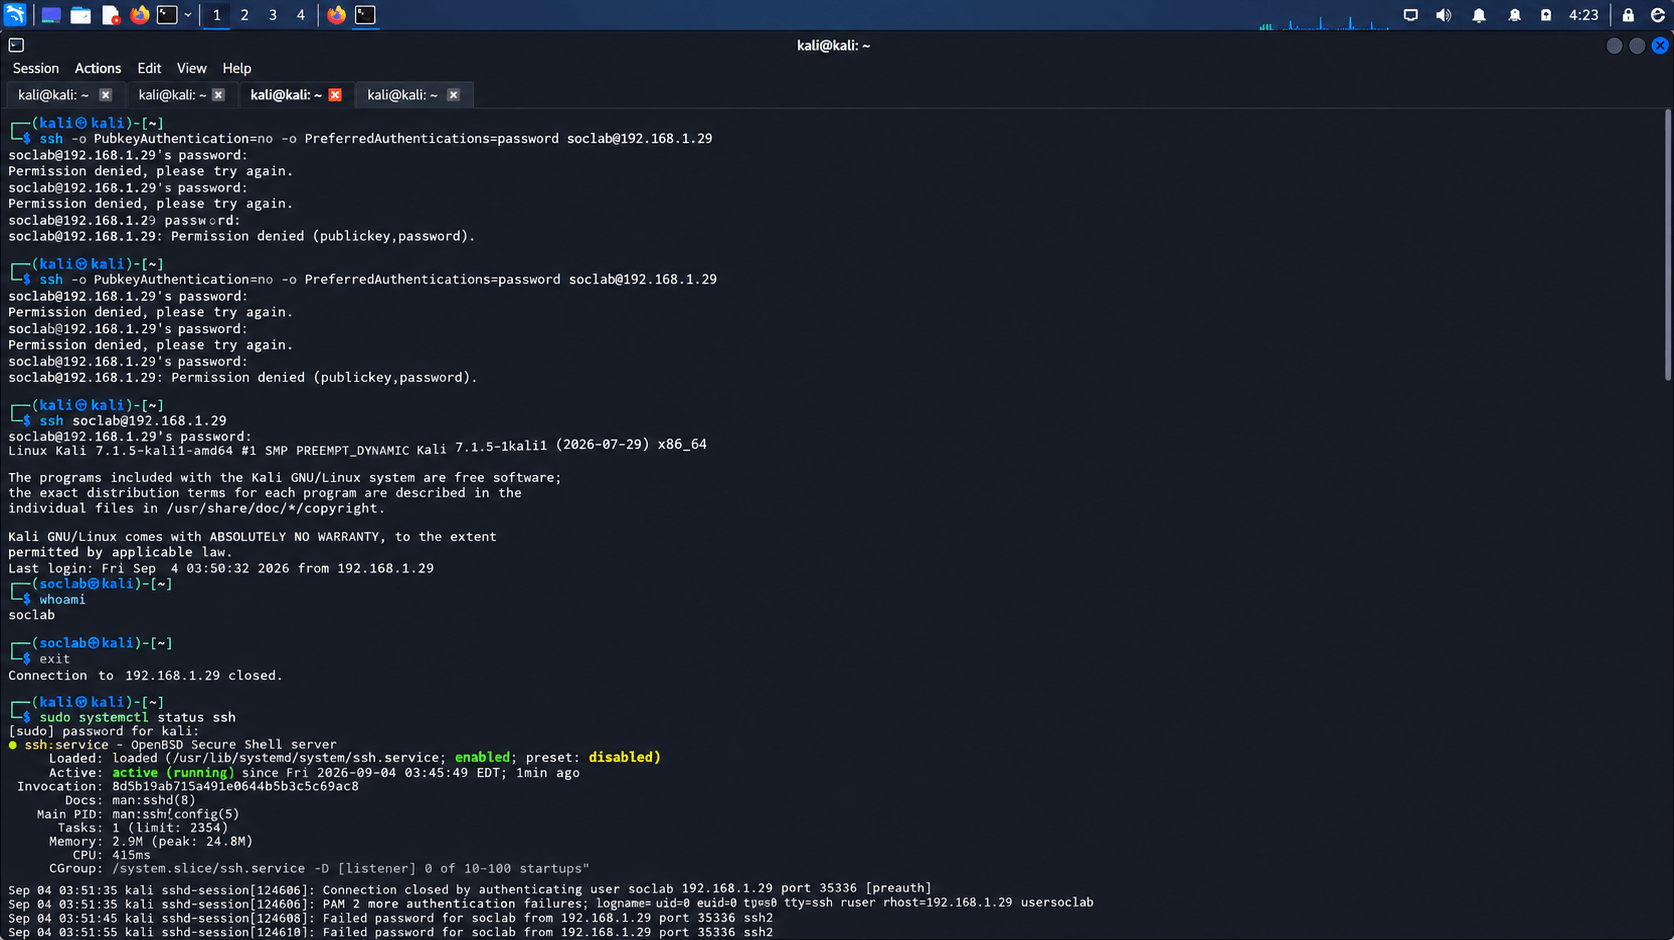
Perform activities such as:
-
Multiple failed login attempts.
Steps
-
Login using a test account.
-
Create/delete a test file.
-
Start or stop a test service.
-
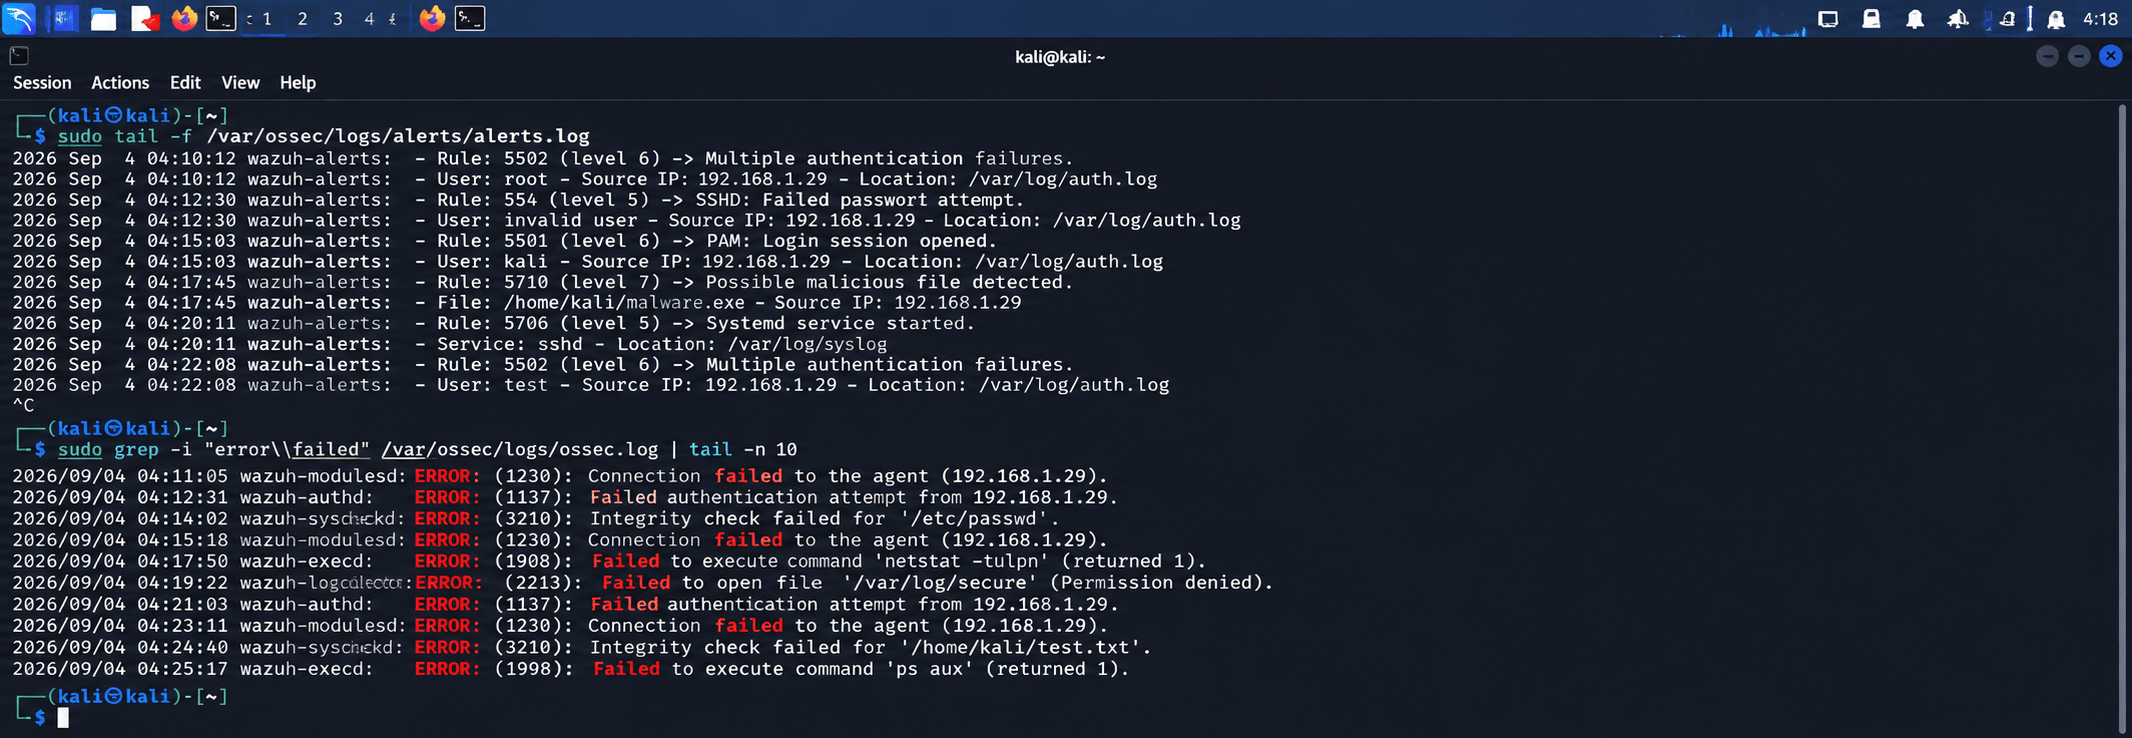
Monitor the SIEM dashboard.
-
Identify the events generated by these activities.
Task 3: Detect and Analyze an Alert
Determine whether an alert represents suspicious activity.
1
a
-
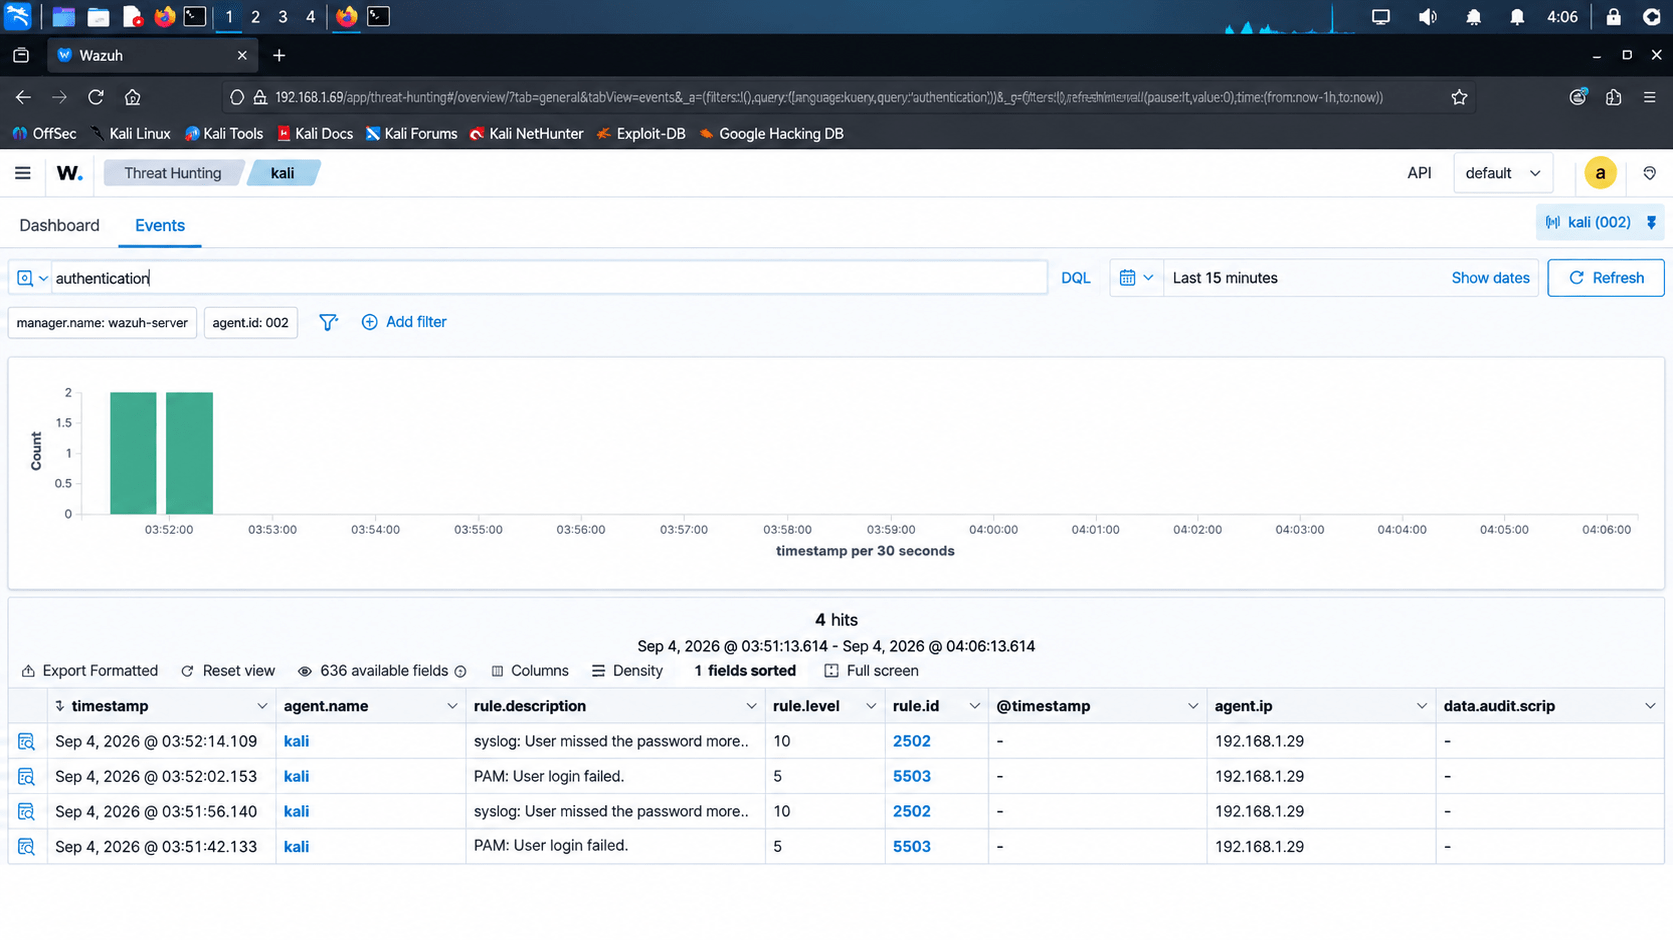
Select a generated alert.
-
Examine:
-
Source IP
-
Username
-
Timestamp
-
Event type
-
Severity
-
Number of attempts
-
Steps
-
Select a generated alert.
-
Examine:
-
Source IP
-
Username
-
Timestamp
-
Event type
-
Severity
-
Number of attempts
-
-
heck related events.
-
Decide whether the activity is:
Normal
OR
Suspicious
OR
Potential Incident
Task 4: Take Basic Defensive Action
Understand how a SOC analyst responds to suspicious activity.
1
a
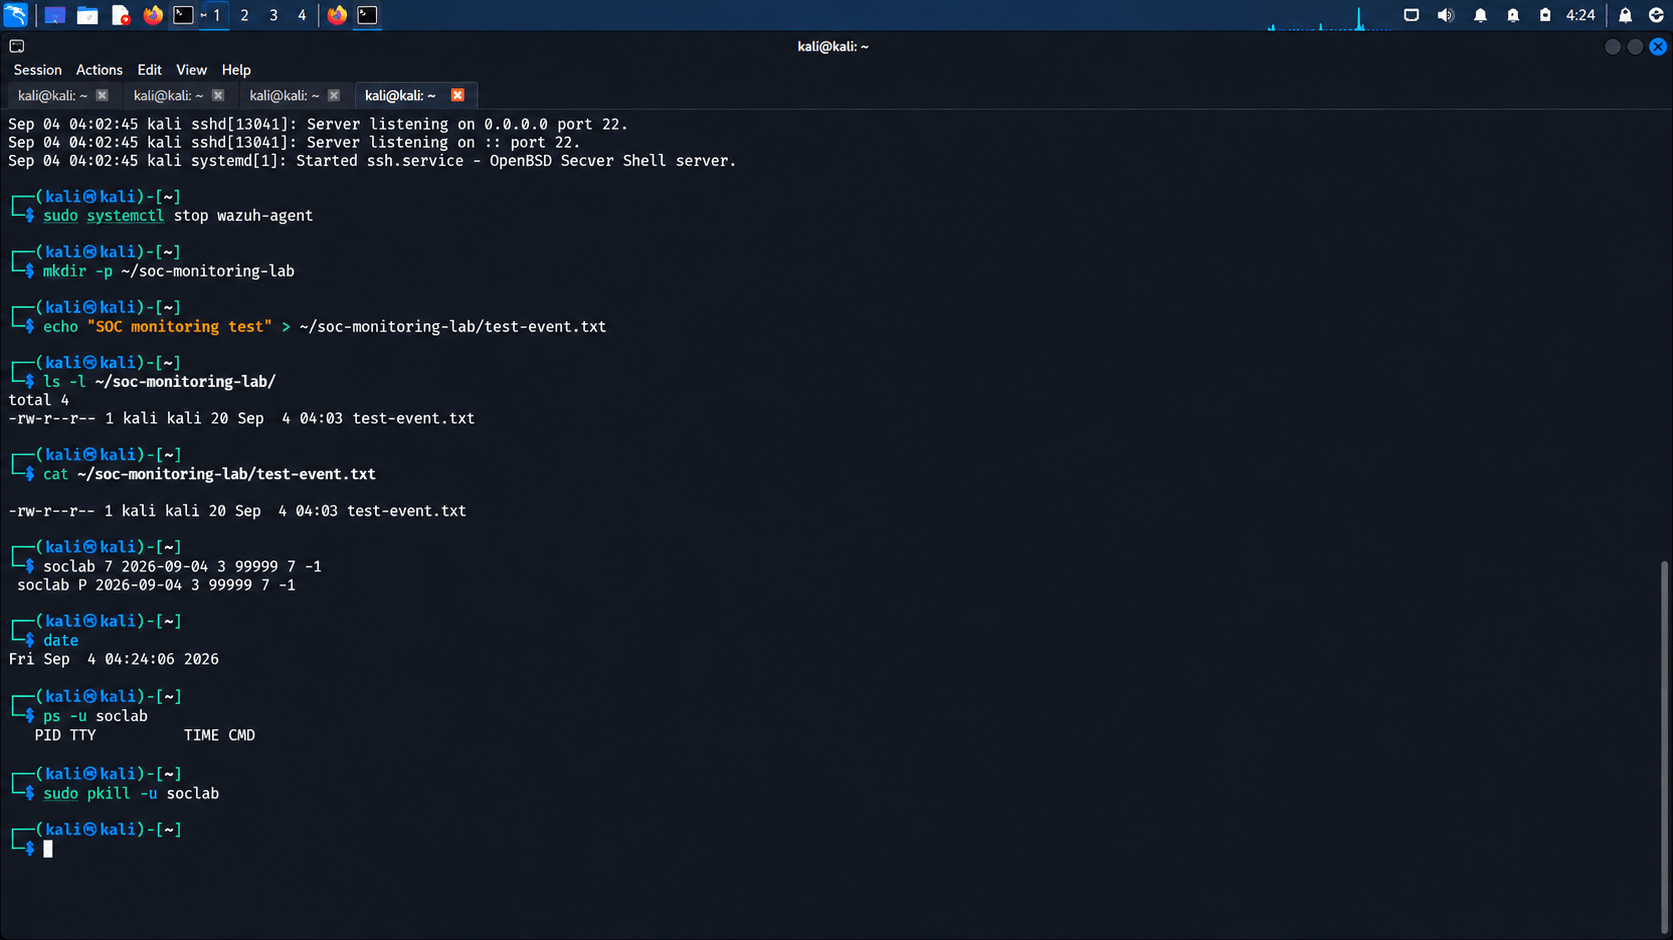
Based on the investigation, perform an appropriate action in the training environment, such as:
-
Disable a test account.
-
Reset a test password.
-
Block a test IP.
-
Isolate a test endpoint.
Steps
Based on the investigation, perform an appropriate action in the training environment, such as:
-
Disable a test account.
-
Reset a test password.
-
Block a test IP.
-
Isolate a test endpoint.
-
Apply the selected action.
-
Continue monitoring the SIEM.
-
Verify whether the suspicious activity stops.
Task 5: Document the Security Event
Create a basic security monitoring report.
Record:
1
| Field | Example |
|---|---|
| Event ID | SOC-001 |
| Alert | Multiple Failed Logins |
| Source | TEST-PC01 |
| Severity | Medium |
| Investigation | Multiple failed attempts detected |
| Action Taken | Test account disabled |
| Status | Resolved |
| Analyst | Student Name |
Click to view : SOC incident report
Great job!
You have successfully completed your Real-Time Security Monitoring lab.
In this lab, you have: Performed real-time security monitoring, Monitored security events, Identified suspicious activities, Analyzed potential threats
You are now ready to move to the next stage of SOC monitoring and threat detection.
Checkpoint
Next-Lab Preparation
Topic : SOC Fundamentals
1) Introduction to Security Operations Center (SOC)
2) Roles and responsibilities of a SOC analyst
3) Security monitoring fundamentals